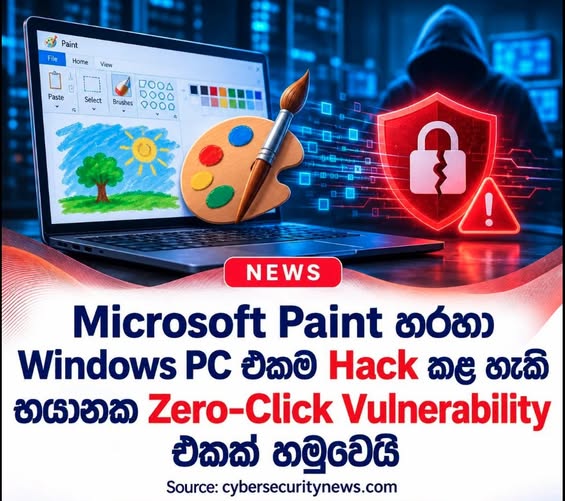
A high-severity security vulnerability has been discovered in Microsoft Paint, one of the most widely used default applications on Windows computers. Tracked as CVE-2026-83844, this flaw could allow a remote attacker to execute arbitrary malicious code on a targeted system under specific conditions.
Because Microsoft Paint comes pre-installed on millions of Windows devices, security researchers and system administrators are urging users to verify their app versions immediately, even if standard Windows Updates are already enabled.
Vulnerability Overview: CVE-2026-83844 at a Glance
| Attribute | Details |
|---|---|
| CVE Identifier | CVE-2026-83844 |
| Affected Software | Microsoft Paint (Windows) |
| Vulnerability Type | Remote Code Execution (RCE) |
| Root Cause | Out-of-Bounds Read (CWE-125) |
| CVSS 3.1 Base Score | 8.1 (High Severity) |
| Attack Vector | Network-based (Zero-Click potential) |
| Disclosure Date | October 13, 2026 |
| Patched Version | 11.2609.401.0 or later |
The Danger of a "Zero-Click" Remote Code Execution (RCE)
CVE-2026-83844 is classified as a Remote Code Execution (RCE) vulnerability. According to technical advisories from Microsoft, the flaw utilizes a network-based attack vector that requires neither physical access to the target machine nor elevated user privileges.
Most concerningly, under specific attack conditions, a system can be compromised without any interaction from the user. In cybersecurity, this is known as a Zero-Click Attack. Unlike traditional phishing or malware campaigns that rely on tricking a user into clicking a malicious link or opening a compromised file, a zero-click exploit can compromise a vulnerable machine silently in the background.
Technical Root Cause: Out-of-Bounds Read (CWE-125)
At the core of this vulnerability is a memory handling flaw categorized as an Out-of-Bounds Read (CWE-125).
In simple terms, this occurs when the software attempts to read data past the boundaries of the memory buffer allocated to it. If successfully exploited by a threat actor, this improper memory handling can be leveraged to run unauthorized code on the victim's computer. A successful exploit threatens the core pillars of system security:
- Data Confidentiality: Unauthorized access to sensitive personal or corporate files.
- System Integrity: Unapproved modification of system files or installation of secondary malware.
- System Availability: Potential system crashes, lockouts, or resource hijacking.
Due to the ease of remote exploitation and the severity of the potential impact, CVE-2026-83844 has been assigned a CVSS 3.1 score of 8.1, placing it firmly in the High Severity category.
Why Standard Windows Updates Might Not Be Enough
Microsoft officially disclosed CVE-2026-83844 on October 13, 2026, and has already released an official security patch to address the flaw.
However, there is a critical catch for Windows 11 users: installing standard Windows OS updates does not automatically guarantee that Microsoft Paint is patched. Modern versions of Microsoft Paint are distributed and updated independently through the Microsoft Store. According to current reports, the vulnerability is resolved in Microsoft Paint version 11.2609.401.0 and higher.
How to Check and Update Microsoft Paint
To ensure your system is protected against CVE-2026-83844, follow these steps to verify your current version and force an update:
- Check Your Current Paint Version:
- Open Microsoft Paint.
- Click the Settings (gear icon) in the top-right corner.
- Scroll down to the About section and verify that your version number is 11.2609.401.0 or higher.
- Update via the Microsoft Store:
- Open the Microsoft Store app on your Windows PC.
- Click on Library in the bottom-left corner.
- Click the Get updates button at the top right to download and install the latest patch for Microsoft Paint and any other built-in Windows apps.
Frequently Asked Questions (FAQ)
What is CVE-2026-83844? CVE-2026-83844 is a high-severity Remote Code Execution (RCE) vulnerability affecting Microsoft Paint on Windows systems, caused by an Out-of-Bounds Read memory error (CWE-125).
Do I need to open a malicious file in Paint to be hacked? Not necessarily. Technical assessments indicate that under specific network-based conditions, this flaw can be triggered as a "zero-click" attack, meaning no user interaction is required to expose the system to risk.
Which version of Microsoft Paint fixes CVE-2026-83844? Updating Microsoft Paint to version 11.2609.401.0 or later via the Microsoft Store completely resolves the vulnerability.
Tags: #CyberSecurity #Microsoft #Windows11 #MicrosoftPaint #ZeroClick #RCE #CVE202683844 #InfoSec #WindowsUpdate