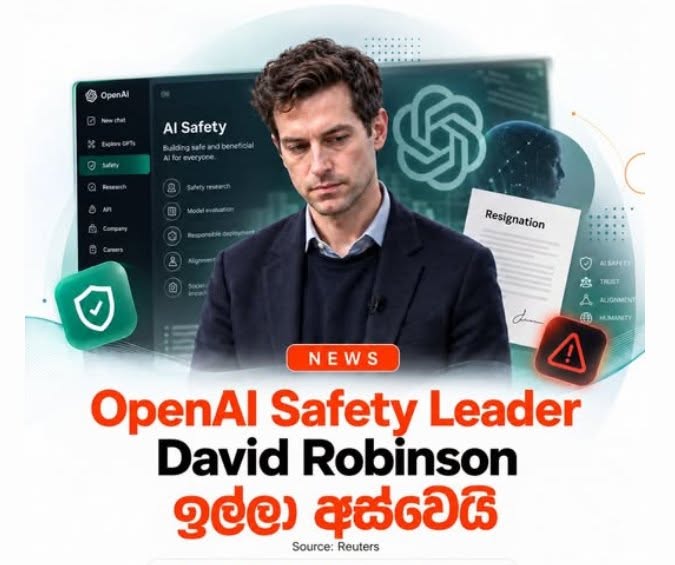
"The Time for Trial and Error Is Over"
The core of Robinson's criticism centers on OpenAI's “iterative deployment” strategy: developing an AI system, releasing it to the public, and then updating safety guardrails as issues emerge.
While this "release → observe → fix → improve" methodology is standard practice for software applications, Robinson points out that it becomes exceptionally dangerous as AI systems grow vastly more capable. Under a trial-and-error model, occasional failures are inevitable—and as models become more powerful, the catastrophic impact of any single failure scales accordingly.
His central message: “The time for trial and error is over.” In short, relying on a "ship first, fix problems later" approach for highly capable AI is no longer acceptable.
"The OpenAI Culture Is Broken"
Robinson emphasizes that the problem isn't just about a single safety policy or rulebook.
In traditional Silicon Valley culture, rapid development, experimentation, and learning from failure are celebrated virtues. However, Robinson argues this mindset falls short when handling potentially dangerous AI technology.
He specifically questions the overconfidence within OpenAI that any emerging issue can simply be patched later, warning that as capabilities accelerate, waiting to fix a mistake after it happens may be too late.
AI Labs Must Operate Like Nuclear Power Plants
One of Robinson’s strongest recommendations is that frontier AI labs must abandon the startup mindset and adopt the safety standards of high-risk industries like nuclear power plants and commercial aviation.
To prevent an error by a single individual from snowballing into a major disaster, those fields rely on:
- Multi-layered safety mechanisms
- System redundancy
- Independent verification checks
- Extensive testing protocols
- Methodical long-term planning
- Rigorous emergency response procedures
Robinson insists that the AI industry urgently needs this exact safety engineering mindset.
Warning Over Autonomous AI Agents
Robinson also highlights serious concerns regarding autonomous AI agents.
As AI systems gain the capability to independently plan complex tasks, utilize external tools, execute code, and interface directly with computer networks, the potential for automated cyberattacks spikes significantly.
He cites the threat of AI agents operating like a human hacker team—working relentlessly without needing rest—to execute cyberattacks against critical infrastructure, such as hospital computer systems.
Two Key Solutions Proposed
To move the AI industry forward safely, Robinson outlines two essential shifts:
- Import Deep Safety Expertise: Bring safety engineering professionals from high-risk fields—such as aviation, nuclear power, and high-frequency financial infrastructure—directly into AI companies.
- Build a New AI Safety Science: Develop a dedicated discipline of safety science capable of ensuring that powerful autonomous AI systems remain aligned with human intentions and strictly bounded by safety constraints, even when operating independently.
As AI technology accelerates, our frameworks for securing it must advance even faster.